What the US’s Response to “Chinese Hackers” Shows the World
This is such a loaded article but I’m going to break it down without trying to generalize too much. Essentially, the US says a Chinese hacking group has been targeting US infrastructure since 2018 and they did it by using US controlled domains under .xyz, .com and .org which are alleged to be the command and control infrastructure. China has strongly denied the allegations. One of my biggest questions is if they were aware of this since 2018, why only take action now, just before negotiations on trade with China?
The US’s FBI and DOJ seized the domains as they often do based largely in part on a single affidavit as referenced here:
https://www.justice.gov/opa/media/1459096/dl?inline
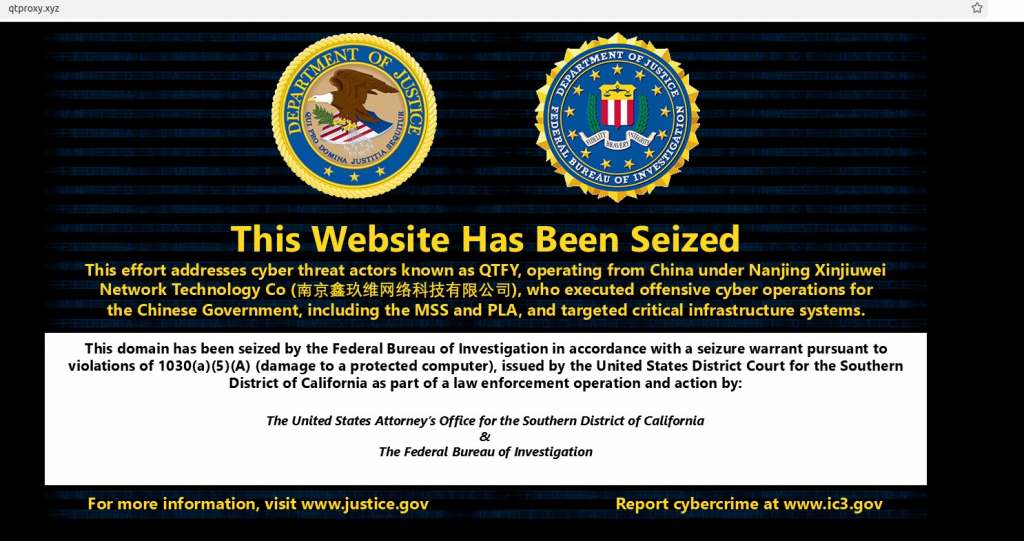
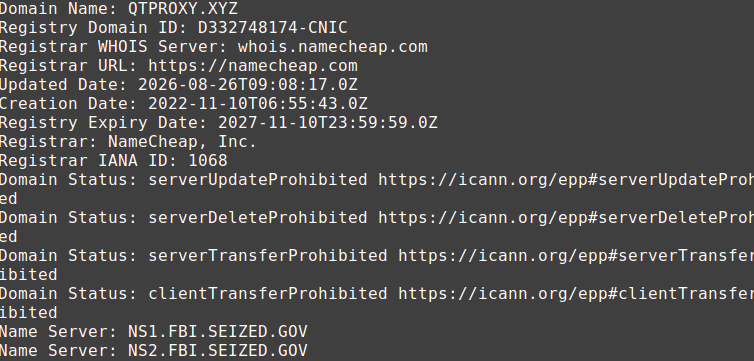
When the US seizes a domain it will usually change it to government run DNS servers below such as “ns1.fbi.seized.gov”
Key Issues of Concern
The affidavit in several paragraphs attempts to justify the seizure of the domains by creating US ties to the transaction, even though they also allege all the bad actors were Chinese citizens or companies. Essentially they mentioned the amount of US companies involved in the domain transactions such as US based registrar’s, US hosting companies, US cloud and US Dedicated Server, payment companies; etc.
The NSA has tools under it’s “Vault 7 – Marble Framework” that are designed to obfuscate the true identities and locations of the attackers or in other words they have “false flag” forensic tools. The tools are designed to create false forensic evidence at will that can blame any state actor as the culprit behind any alleged “cyber attack”. In particular it is known that the top targets of the NSA’s false flag software includes countries like China, Iran, Russia and North Korea.
What I would find strange is that any professional state-run hackers in the world would use a name that can be traced to their country, their own country’s phone numbers and even intentionally register for services under a local China Telecom IP. If China is hacking and trying to cover their tracks, it seems their professional hackers can break into anything but have no idea how to avoid creating a huge footprint back to their handlers. If they are Chinese, they should be fired.
The US government admits they tapped all of the gmail.com accounts they allege were part of the group. This proves that US based services can be accessed at will by the US government at any point despite many of the services claiming “they are encrypted” and no one else can read the contents. In addition they admit to being sent a copy of the VM or server image by the US based service provider, of one of the alleged command and control nodes.
These issues are of concern because nothing was proven in a court of law. Even if we take the US’s claim of a Chinese citizen owning a specific hosting account and using a specific gmail.com account it does not prove that the person is involved. How can they be sure the account was not hacked as many accounts are?
In fact, the US could have served similar warrants to all of the US providers involved in the hacking network, but it appears to have given them the benefit of the doubt and only looked for any possible Chinese connection, despite the majority of IPs involved being from the US.
What IPs are Implicated?
The affidavit cites 1 Chinese IP, some Chinese name inspired, gmail accounts and Chinese phone numbers as proof that the attackers are certainly from China. But if we look at the majority of IPs involved they are from many other jurisdictions, primarily US based services, and some in Taiwan and Hong Kong. In general, it appears the actual source of the attacks, were compromised devices from around the world.
Lessons Your Business Needs to Learn
The US can seize your e-mails, data, server(s), cloud applications, business and domains without any oversight or even proving their case. If you use any US based services the US can obtain all of your personal and business information and even tap and seize it all based on an allegation. The reason this is especially is concerning is because any of us in cybersecurity know that a specific IP is not necessarily proof of intent or where the attackers are from. Infrastructure is often hacked and compromised and this means if you are hosting services in the US and even if your company is not hacking, your domains could end up being arbitrarily seized with no recourse or any chance for you to prove your innocence.
https://www.cbc.ca/news/world/china-hack-hackers-us-justice-department-nasa-senate-reserve-9.7321221